Practitioner-led Information Security

Cyber & Technology
Consultancy

Steady in uncertain waters. For businesses, charities, family offices and private clients. ISO/IEC 27001, Cyber Essentials Plus, Microsoft 365 security, third-party risk and AI governance, from someone who has run the function.

  • 4× Cyber Essentials Plus, 2022 to 2025
  • 93/93 ISO 27001 Annex A controls mapped
  • 400+ devices managed in Microsoft 365 over six years
  • ~180 suppliers risk-managed

From governance questions to working outcomes

Fractional technology leadership, security governance, tool delivery and AI governance for businesses, charities, family offices and private clients. Practical, evidence-led, from a practitioner who has run the function.

Security and supplier overviewIllustrative
85%
Controls documented
72%
Evidence collected
94%
Owners assigned
Access reviewsPassing
Supplier contract clausesIn review
Incident response planAction needed
Supplier due diligence
AI governance overviewIllustrative
100%
Staff under policy
68%
Tools risk assessed
55%
Use cases logged
AI use policyPassing
Supplier AI questionsIn review
Leadership reportingAction needed
Tools assessed
Fractional technology governance leadership
Senior, hands-on leadership for a defined programme or period of change: setting direction, aligning stakeholders and leading delivery teams. Our experience includes building an IT function from scratch at a fast-growing FCA-regulated business.
Related work and reading
Fractional leadership IT function build Technology strategy Nearshore teams
Security and supplier governance
A security management system and supplier programme that stand up to review. Our experience includes a 22-policy suite, all 93 Annex A controls mapped, four consecutive Cyber Essentials Plus certifications, and about 180 suppliers managed to PRA SS2/21.
Related work and reading
ISMS build Cyber Essentials Plus ISO 27001-aligned ISMS Third-party risk
AI-assisted workflow and tool delivery
Turn an operational or governance problem into a tested, working application. We have built live demonstrators for impact assessment, supplier risk scoring, programme tracking and service-signal correlation, from problem to working build in weeks.
Related work and reading
Working demonstrators Internal tools Engineering handover
AI governance and assurance
Make AI use visible, auditable and defensible. Our experience includes writing a first AI use policy in March 2023 and rolling out Copilot and Claude to 420+ staff under policy and controls, with reporting to the executive leadership team.
Related work and reading
AI policy Impact assessment Supplier assurance Evidence
Secure Microsoft 365 for small private organisations
Email, documents, passwords and devices on one well-protected platform, set up properly and kept secure, for family offices, small practices, trusts and other organisations without a security team. Our experience includes six years running a Microsoft 365 estate of 400+ devices, including Intune, Defender and Purview. See the service.
Related work and reading
Family offices Microsoft 365 Device management Cyber Essentials
Not sure where you stand?Take our free Cyber Health Check. Answer a few plain-English questions in about three minutes and see what we would fix first.
Check your cyber health

You might need us if...

Your information security function is informal or exists mainly on paper

Whether you are starting from scratch, working towards a more formal ISMS, maintaining Cyber Essentials Plus, or preparing for a regulatory review, and do not have the internal expertise to run it.

Security and supplier governance →
Your teams are using AI tools and no one has written a policy, assessed the risk, or told the board

Shadow AI is a risk most organisations underestimate until it becomes a problem. The exposure from unmanaged AI tool use is greater than many businesses realise, and it's growing.

AI governance and assurance →
Your vendor base has grown faster than your ability to review it

You have limited visibility beyond your immediate suppliers, no clear process for managing questionnaires at scale, and no reliable way to demonstrate vendor compliance when a regulator, investor, or client asks.

Security and supplier governance →
You have had an incident, or a near-miss, and it has changed the conversation

A breach, a serious outage, or a supplier failure has made clear that your governance was not where it needed to be. The time to build resilience is before the next one, not after it.

Security and supplier governance →
Your board is asking questions about digital risk that no one can confidently answer

Cyber risk, AI exposure, supplier dependency: these are board-level conversations now. If your organisation does not have a credible answer prepared, that is a gap worth closing.

Security and supplier governance →
You need senior technology leadership for a defined period while you hire, restructure, or navigate a regulatory event

A fractional or interim engagement gives you the expertise when you need it, for a specific programme, a regulatory moment, or an ongoing advisory role, without the overhead of a full-time appointment.

Fractional technology governance leadership →

Discover. Build. Test. Hand over.

01
Frame the real problem
Start with the decision, workflow or risk that matters. Agree the users, constraints and what a useful outcome would prove.
02
Make it tangible
Design practical controls or a working demonstrator. AI-assisted development can accelerate delivery; people remain accountable for the judgement and requirements.
03
Test it with users and owners
Check the whole journey, not just a polished screen: edge cases, evidence quality, operational fit and what remains unresolved.
04
Transfer or lead delivery
Hand the evidence, design and code to an engineering team, or help lead the team that takes the work into service.
Advisory
A focused assessment, governance design or decision-ready recommendation.
Demonstrator
A bounded, tested example that makes an idea concrete before a larger commitment.
Handover
Documentation, architecture and known limitations for the team taking the work forward.
Leadership
Fractional support or delivery leadership where a team needs direction and ownership.

What practical governance can look like

Some examples come from earlier in-house roles and are anonymised; the demonstrators are built to show our approach, using fictional or sandbox data. Request a walkthrough to discuss the design decisions and limitations. More demonstrators (Control Evidence, Signal Ledger and a HubSpot setup) are in Labs.

Working demonstrators AI governance Human-authored judgement

The IQ series: three working apps, one fictional lender

What it is We built three small apps that cover the core of AI governance for a firm that uses someone else's AI model. All three use the same fictional UK lender, Northbridge Credit, which buys its credit-decision model from a supplier.
Show the full caseHide the full case

Why it is useful

  • It turns an AI governance standard into a record a board can read in minutes.
  • Missing evidence and unfinished decisions come first, not hidden inside a score.
  • Every open item ends with a named owner and a next action.

What it does not do

  • The software never makes the judgement. People write the decisions; the apps organise them and flag what is missing.
  • The companies and data are invented. These are educational demos, not legal advice or a compliance check.
  • The three apps are separate and do not share data.

Try it: Follow the 15-minute walkthrough → Or read the one-minute guide, or see how they were built and tested.

First look: what each one is for

GovernIQ home page: “Know what applies. Show why.”, with a card showing three steps: define scope, record the decision, see open work, and a button to explore the fictional Northbridge example.
GovernIQ Live fictional demo
SupplierIQ home page: “Know what the supplier provides. See what remains yours to own.”, a four-step diligence thread, and a note that the completeness measure does not rate a supplier.
SupplierIQ Live fictional demo
ImpactIQ home page: the headline “Understand an AI system's impact. See what needs a decision.”, a four-step decision path, and a button to explore the fictional Northbridge Credit example.
ImpactIQ Live fictional demo

The story, in five steps

  1. ScopeGovernIQLive fictional demo

    Northbridge starts by recording what its credit-decision model covers, who owns it and which controls apply, each with a reason. Fictional example.
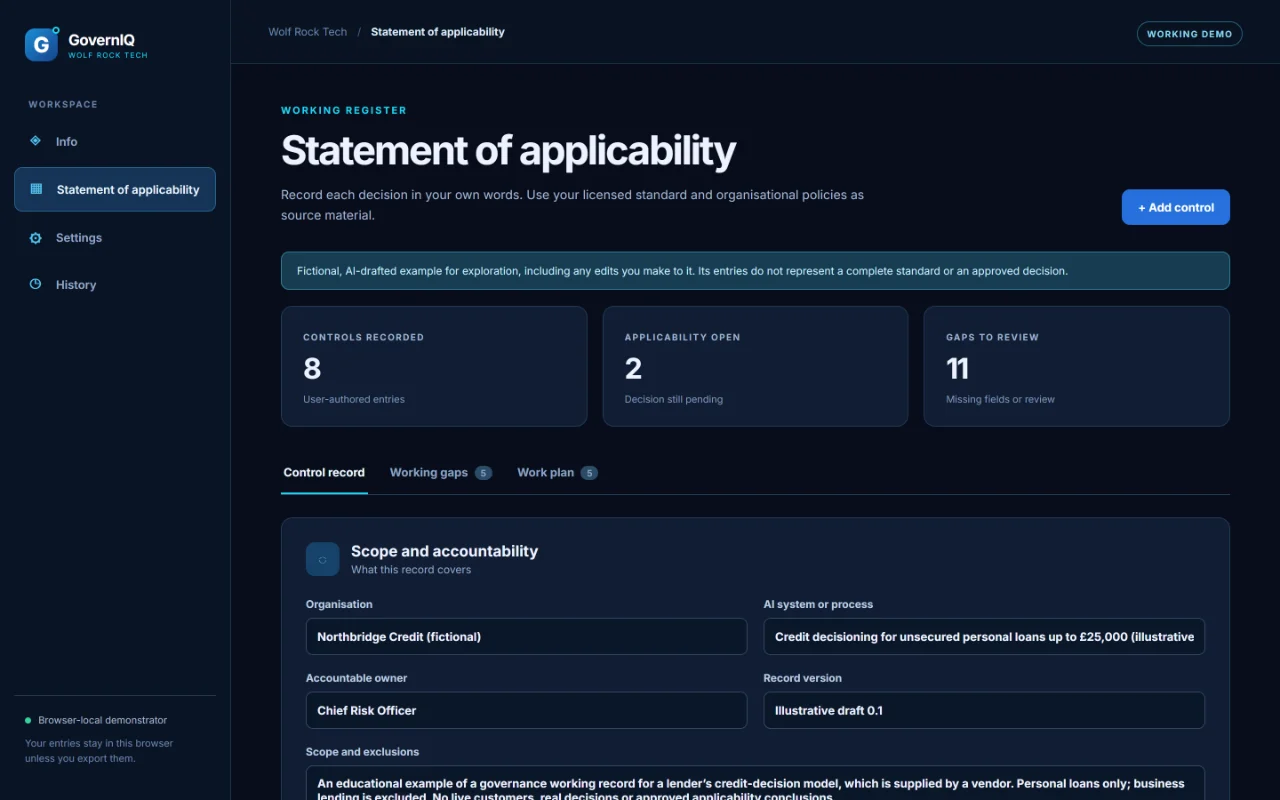
    GovernIQ statement of applicability for the fictional Northbridge Credit: three counters (8 controls recorded, 2 decisions open, 11 gaps to review), the Control record, Working gaps and Work plan tabs, and the scope and accountability panel.
    Open full-size image ↗
  2. The vendorSupplierIQLive fictional demo

    Meridian’s model makes the decisions, so Northbridge checks the supplier before relying on it. The completeness measure describes the diligence record, not the supplier. Fictional example.
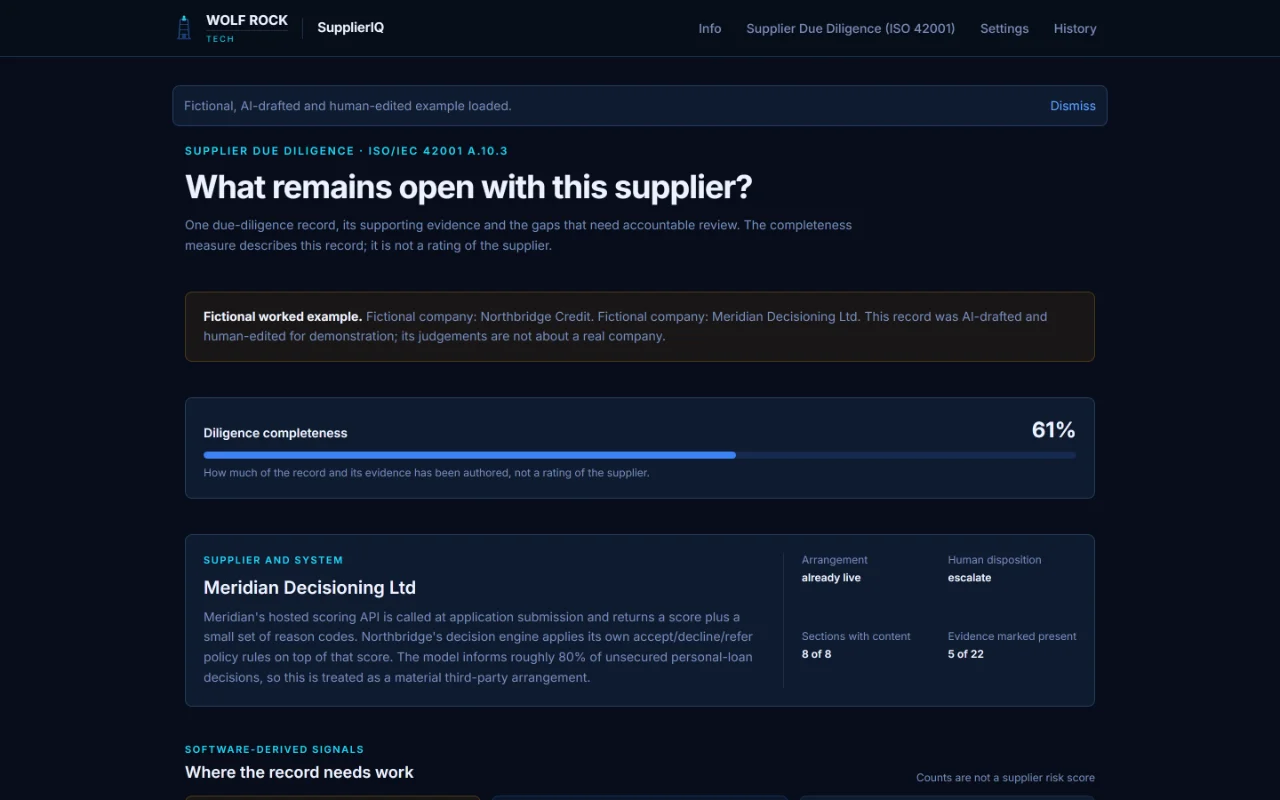
    SupplierIQ results for the fictional supplier Meridian Decisioning Ltd: “What remains open with this supplier?”, a fictional-example notice, a diligence completeness meter at 61% labelled as describing the record rather than rating the supplier, and a summary showing 8 of 8 sections with content and 5 of 22 evidence items marked present.
    Open full-size image ↗
  3. The impactImpactIQLive fictional demo

    One human-written assessment of the credit model’s effect on customers, showing what still needs a decision.
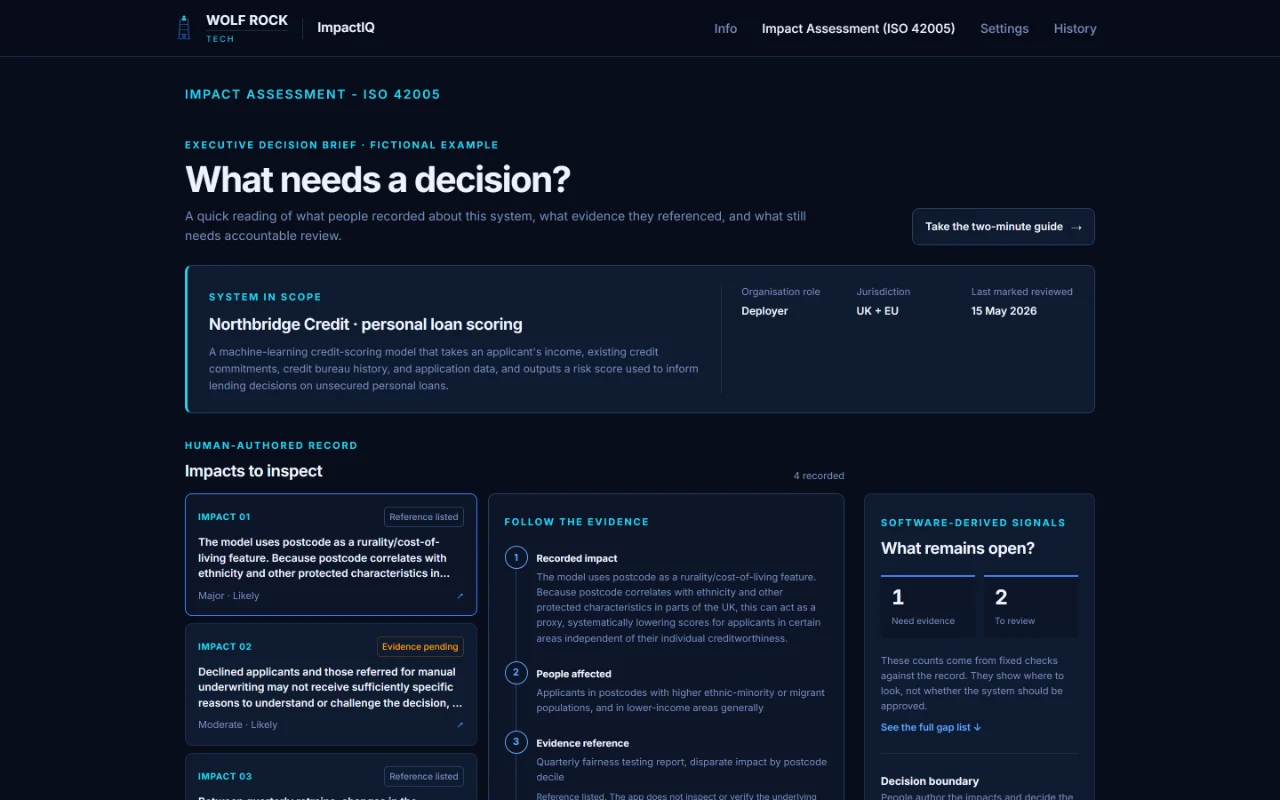
    ImpactIQ executive decision brief for the fictional Northbridge Credit personal loan scoring model: “What needs a decision?”, the system in scope, the impacts to inspect and what remains open.
    Open full-size image ↗
  4. The harmsImpactIQLive fictional demo

    The matrix plots only the harms people recorded. It does not decide the risk.
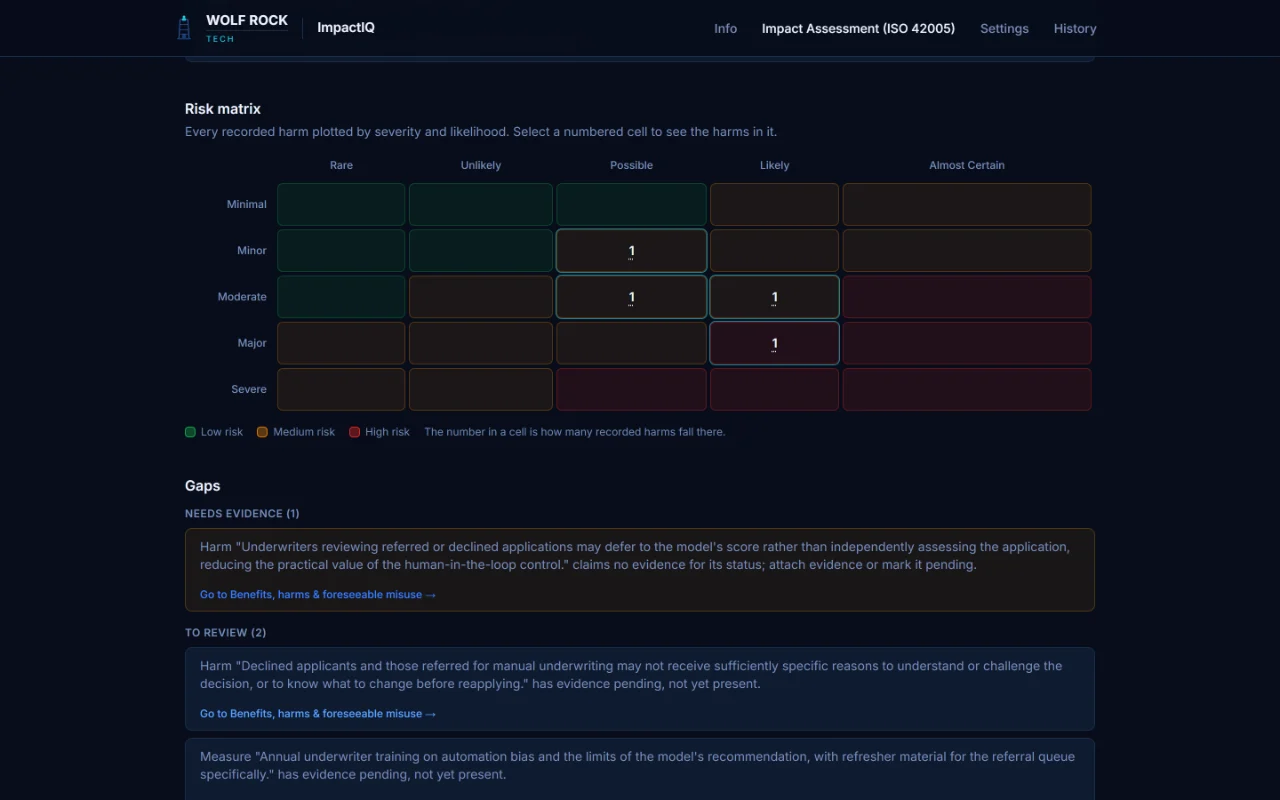
    ImpactIQ risk matrix plotting four recorded harms by severity and likelihood, with a legend and a list of gaps beneath it.
    Open full-size image ↗
  5. What is still openGovernIQLive fictional demo

    The record ends with open work grouped by owner, unassigned items first. Nothing is scored.
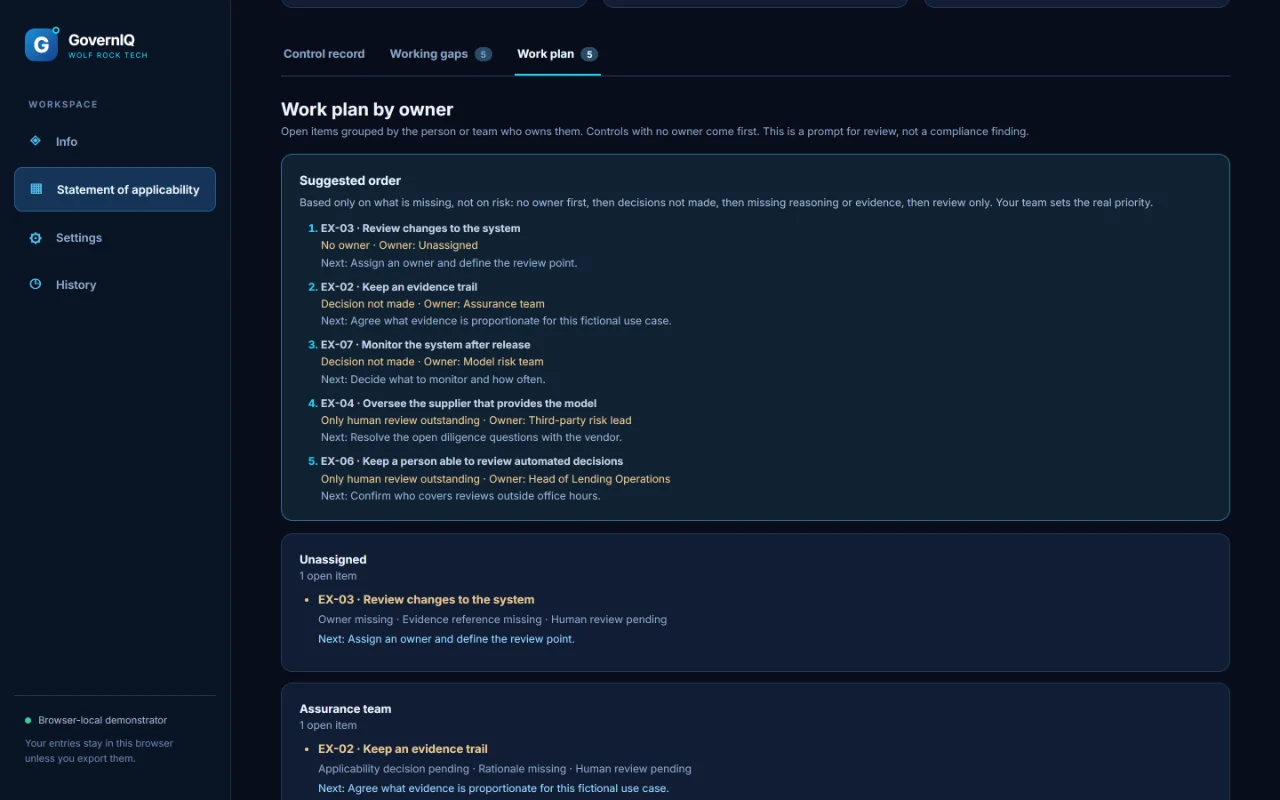
    GovernIQ work plan: a numbered suggested order of the five open items, starting with EX-03 because it has no owner, with the rule stated, followed by the items grouped by owner with their next actions.
    Open full-size image ↗

All three are live fictional demos. They are separate apps with no shared data, accounts or integration, and none of them makes a compliance determination.

Supplier due diligence Anonymised Independent review

Reviewing an early-stage security vendor: what the evidence did and did not support

The question A small organisation wanted to know whether a very young supplier of AI-enabled security services was safe to rely on.
Show the full caseHide the full case

We produced a short, sourced desk review: who the company is and who owns it, what the product does, who it competes with, what it claims about security and compliance, and its funding and reputation. It ended with a four-level risk rating and a recommendation. Every fact was labelled by where it came from: the vendor’s own material, an independent source, or partner and reseller marketing. Those are not equivalent, and the report said so.

The product was real and working, and nothing suggested a sham. But every claim that matters for trust beyond “it exists” traced only to marketing, never to a certificate, a named auditor or an official register. Claim strength grew with distance from the source: the vendor’s own wording was cautious, while resellers described the same thing as fully compliant. One claimed status was not something a supplier of that kind holds about itself, so the useful question was whether its work would meet the underlying requirement. For a young company, finding no bad news is a weak signal, and we said so rather than calling it a clean bill of health.

We rated the risk elevated and did not recommend approval yet. If a pilot was still wanted, the steps were to verify certifications directly with the issuing bodies, confirm which legal entity would hold the contract and the data, take customer references, and re-review in six to twelve months.

This was an independent, desk-based review carried out as a favour, not a commissioned client engagement, and we had no contact with the vendor. Details have been removed so the company cannot be identified. It is not legal advice, an audit or a certification.

Prior employment Anonymised Leadership experience

Building an ISMS and leading a readiness programme

In a prior role at a regulated financial-services platform, the experience behind Wolf Rock Tech built the information security management system and led its ISO 27001 readiness programme. That work spanned policy, control ownership, evidence and coordination across business functions while the organisation continued to grow.

The outcome: a 22-policy suite, all 93 Annex A controls mapped, 85% of control documentation in place at handover, and four consecutive Cyber Essentials Plus certifications (2022 to 2025). The programme paused on business priorities, not on quality.

This is an example of earlier employment experience, not a Wolf Rock Tech client engagement. The programme was not represented as a completed certification or a fully achieved readiness state.

Wolf Rock Tech Labs
Exploring product ideas and real-world workflows beyond the consultancy demonstrators. Concepts remain research or development work until they have been tested with users.
Explore Wolf Rock Tech Labs

We keep you off the rocks.

Tell us about a governance challenge, a workflow worth improving, or a leadership gap. You can also request a walkthrough of the demonstrators.

An introductory conversation is a good place to establish whether there is a useful fit.

Message received. We'll be in touch within one working day.

Prefer email? info@wolfrocktech.ai